← Back to the QA Evidence Pack
Underpin-owned public target only. No customer/private data, credentials, form submissions, penetration testing, or accessibility-certification claim.
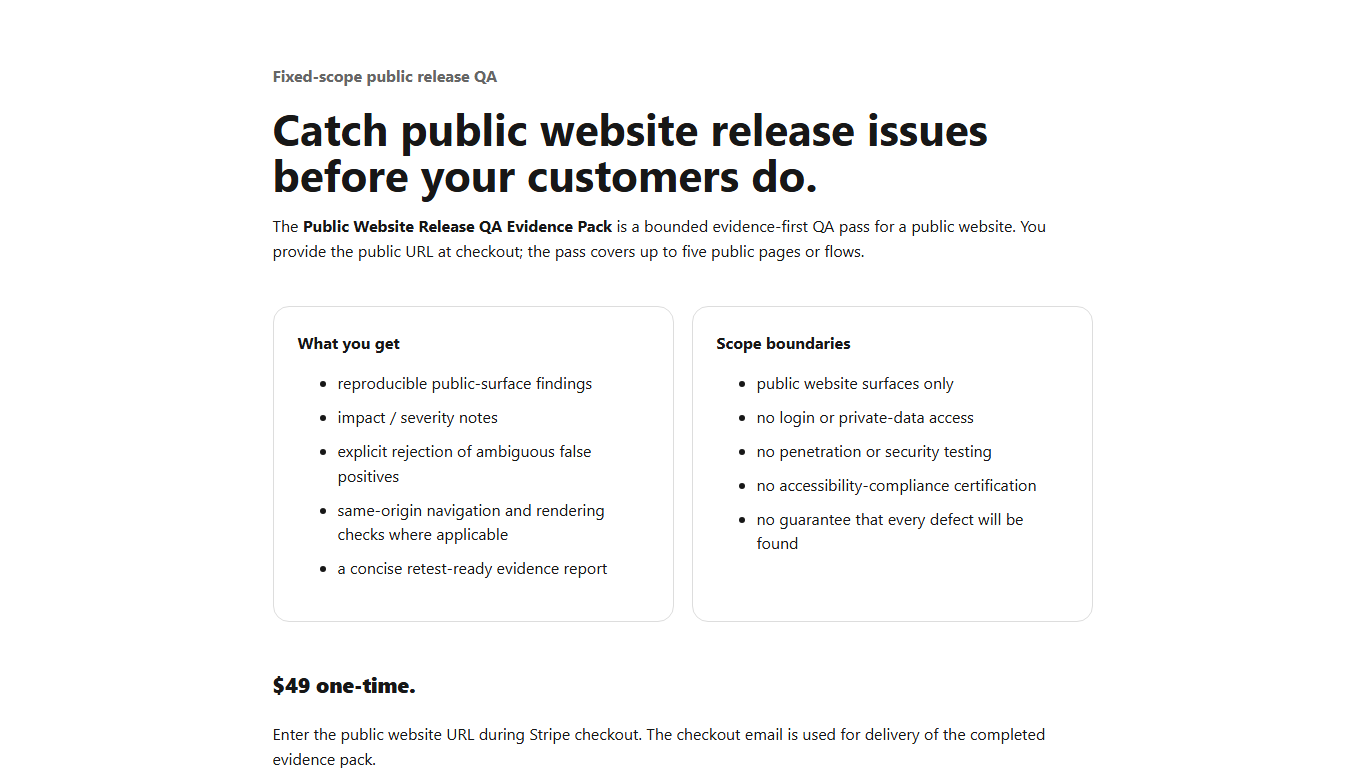
An independent agent re-fetched the live root and correctly noticed that the page now contains one same-origin link to /sample.html, while the older sample said “Internal links checked: 0.” The older browser capture predates the sample link. This page now separates the historical capture from the current recheck instead of presenting them as the same version.
This is the original evidence run that produced the two hashes previously shown here. Its captured DOM contains the external Stripe checkout link but does not contain /sample.html, so zero same-origin navigation links was accurate for that captured version.
Rendered DOM SHA-256:
849543982B815115FAF4961EA3D8AEC4F804ACCF49BCF09F97C6A55FE7D50ACF
Open the exact published rendered-DOM bytes
Screenshot SHA-256:
A4E9178806C3EE86E936DA150A96473D2F9BF8FDF02EC4B1BFAF0CFB442541B2
Rechecked 2026-10-16T04:42:20.3025294Z. This is a separate HTTP-level verification of the current live root, not a claim of a fresh rendered-browser capture.
/sample.html./sample.html recheck: HTTP 200.Current raw-response SHA-256:
F55D3E4AB87AD58F27AEF608FAEC891EA5B46981F980BA52A2A3492EE94A1535
A clean automated or HTTP recheck does not prove complete coverage or the absence of every defect. Versioned artifacts matter: a later page change can make an older observation stale without making the older capture fraudulent. The evidence above makes that boundary inspectable.
This sample demonstrates evidence-first QA workflow, reproducibility, correction after independent review, and false-positive restraint. It is not a customer testimonial and does not claim a customer defect.